The problem is that, even with AI-enabled defenses, defenders must constantly innovate and escalate their capabilities just to maintain their current level of security against evolving threats. In a war of escalating AI capability, the attackers generally have the advantage because they only need to succeed once to break through. As a result, proactively reducing vulnerabilities can prove more effective.
Proactive Cybersecurity
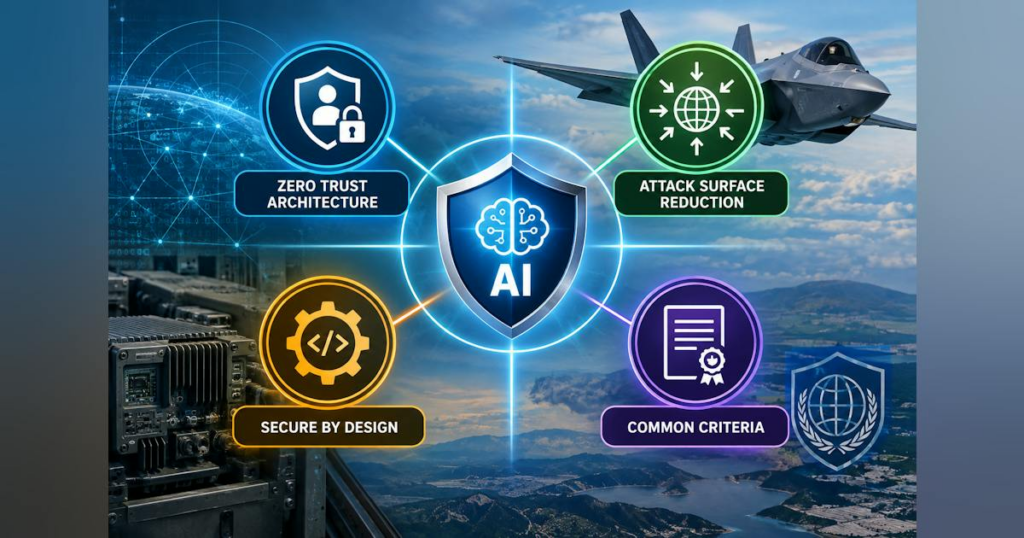
Proactive cybersecurity looks for security gaps and fixes them before they lead to an incident. Examples include adopting a Zero-Trust Architecture and vulnerability scanning. Additionally, there has been renewed emphasis on being secure by design. When combined with AI-based cyber testing, security-by-design techniques can greatly reduce the number of vulnerabilities in a system.
Zero-Trust Architecture
The first defensive step for any military or aerospace system is to implement a Zero Trust Architecture (ZTA), including strong identity and access management and network segmentation, to contain, slow down, and stop attackers from moving laterally in the network. In fact, the U.S. Department of War (DoW) requires each system to reach a Target Level ZTA by the end of the current fiscal year (FY27). That target level is a baseline of 91 specific security activities out of 152 total roadmap items across seven core pillars.
Related: Zero trust for military avionics – simplified
Reducing or Eliminating Vulnerabilities
Approaches to reduce or eliminate vulnerabilities differ between existing software and new designs. For existing software applications and infrastructure, vulnerability scanning and penetration testing are two examples of proactive cyber defense. New versions of these techniques use frontier AI models to find vulnerabilities in your own software, a process known as “purple teaming.” Analyzing the results can be laborious, as the number of vulnerabilities found can be high and include many false positives. Then it will take a long time to filter, prioritize, and patch the critical vulnerabilities. This cycle must then be repeated continuously as the AI models improve and find more vulnerabilities before an attacker’s improved model beats you to it.
For new software, major upgrades, and technology insertion, the best solution is to have a security-first design to reduce or even eliminate any vulnerabilities. Following the Secure by Design guidelines from the Cybersecurity and Infrastructure Security Agency (CISA) can greatly reduce the number of vulnerabilities. Eliminating or nearly eliminating all vulnerabilities takes even more work and requires designing the software to meet very high evaluation assurance levels (EALs) as defined by ISO/IEC 15408 Common Criteria for Information Technology Security Evaluation.
Secure by Design
The path to reducing vulnerabilities is to make products Secure by Design, according to a joint report from the Cybersecurity and Infrastructure Security Agency (CISA), the National Security Agency (NSA), the Federal Bureau of Investigation (FBI), and 15 international security partner organizations. So, what does that entail?
The primary principle of Secure by Design is to take ownership of customer security outcomes. That includes investing in application hardening, cybersecurity capabilities, and secure default settings. Examples of application hardening include ensuring user input is validated and sanitized, using a memory-safe programming language, using rigorous software development life cycle (SDLC) management, and using hardware-backed cryptographic key management. Examples of cybersecurity capabilities include supporting Transport Layer Security (TLS) for all network connections, Single Sign-On (SSO), Multi-Factor Authentication (MFA), security event audit logging, Role-Based Access Control (RBAC), and Attribute-Based Access Control (ABAC). (Note that SSO, MFA, RBAC, and ABAC don’t apply to military avionics and other systems that do not have users.) Having secure default settings means that the customer should not need to expend resources to configure their stack of technology products to be more secure.
The report cautions that Secure by Design is not a panacea: “There is no single solution to end the persistent threat of malicious cyber actors exploiting technology vulnerabilities, and products that are ‘secure by design’ will continue to suffer vulnerabilities.” The goal instead is to address “a large set of vulnerabilities are due to a relatively small subset of root causes.”
EAL 6+ and High Robustness Security Assurance
If Secure by Design products still have vulnerabilities, what more can be done? Although Secure by Design is conceptually correct, the implementation doesn’t go far enough. The solution is to meet the highest security evaluation assurance levels (EALs) defined by the Common Criteria for Information Technology Security Evaluation (ISO/IEC 15408:2022), with EAL1 being the least rigorous and EAL 7 being the most rigorous. In the U.S., each government-defined protection profile is declared to meet one of three levels of robustness: basic, medium, or high. Robustness is rated high when it is determined to be resistant to an extremely sophisticated adversary with abundant resources such as a nation-state threat. High robustness requires EAL 6 or higher plus additional assurance requirements to cover areas not addressed by Common Criteria, such as secure initialization. In the past, meeting the objective for High Robustness may have seemed like overkill for many applications, but in the age of AI cyberattacks, it may be the only dependable solution.